
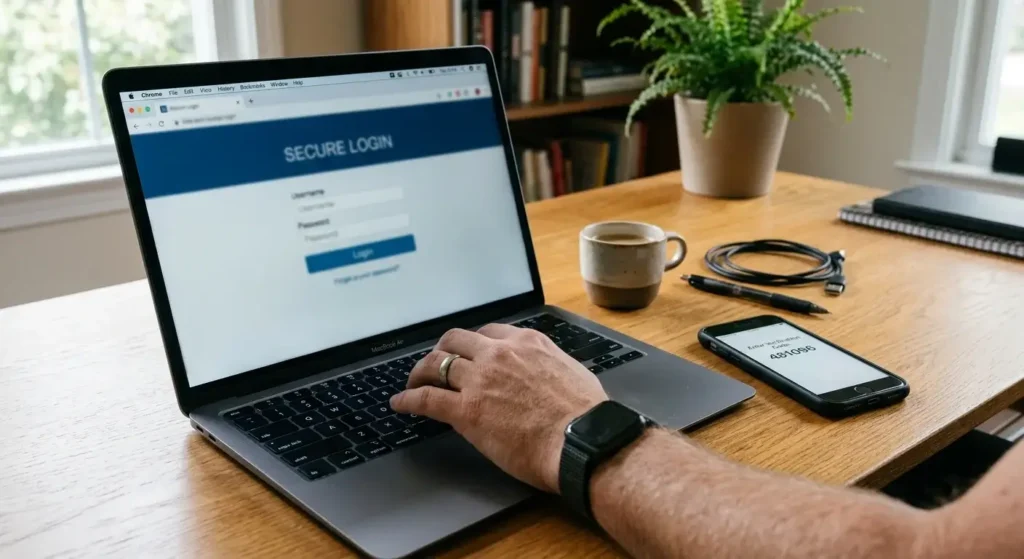
Yes, with a catch. An AI agent can get into a website that needs a login, but in most of the big products today it doesn’t do the sign-in by itself. It stops, hands the browser to you, waits while you type your password or approve the text message, and then carries on. The tools that do sign in on their own are the ones with the most risk attached.
That arrangement is the core of AI agents website automation right now, and a federal appeals court decision from August has made it a legal question as well as a technical one. Here is how the main products handle logins, why codes and passkeys cause trouble, what a logged-in agent can be tricked into doing, and what the court actually decided.
How the big products handle a login page
The pattern is similar across vendors: the agent does the browsing, and you do the proving who you are.
OpenAI’s help page for its agent feature says that when a task needs a login, the agent pauses and asks you to take control of its virtual browser. It advises against typing passwords into the chat and recommends the takeover mode for anything sensitive. While you’re in control, the page says ChatGPT doesn’t capture what you type and doesn’t take screenshots. When you hand control back, it tries to pick up where it left off, and it may have to restart the run if that fails. One caution: that page now says the agent is no longer available and points people to ChatGPT Work, so check how your current version behaves before relying on this description. Logins also stick around, since cookies persist between sessions like a normal browser, and OpenAI suggests signing out and clearing remote browser data after anything sensitive.
Google takes a different route in Chrome. According to Google’s support page for auto browse, Gemini in Chrome needs your permission before it signs in to a site, and with that permission it can use Google Password Manager or Sign in with Google. Google says it doesn’t share your passwords with Gemini or with the sites. In the remote-browser mode of its Spark agent, a sign-in page stops the task until you take over and finish it yourself. Google also says Gemini may ask you to take over for finalizing financial transactions, accepting terms of service, or creating an account, and that its safeguards “do not guarantee protection against all risks.” The feature is limited to adults in the US with a paid Google AI plan, so most people can’t try it yet.
Anthropic’s Chrome extension works on a permission model by site. Its published description says you can grant or revoke Claude’s access to specific websites at any time, and that it blocks high-risk categories such as financial services, adult content and pirated content.
So the honest answer to “can it log in” depends on which door you mean. Using a session you’re already signed into is easy for all of them. Typing a password into a fresh login page is where most of them pause for you.
Why codes and passkeys stop an agent
A password is just text, so an agent can in principle type it. Everything layered on top of the password was built to prove a person is there, and that’s where agents hit a wall.
A developer post on login walls, written by a company selling agent verification tools, so read it as one vendor’s framing, lists the obstacles plainly:
- Text message codes arrive on a phone, outside the browser, so the agent can’t see them. Even if it could, the code has to belong to this attempt, arrive in time, and work only once.
- Email codes and magic links move the proof into an inbox. A magic link can be the login action itself, so clicking it does more than reading a code would.
- Passkeys are tied to a device and a site. The post’s advice is to hand off to a human or fail rather than try to work around the prompt.
- CAPTCHAs exist to block automation, and the post recommends stopping and reporting rather than solving one on a site you don’t control.
On passkeys specifically, Corbado, which sells passkey products, argues an agent shouldn’t be able to use one directly, because the sign-in depends on a biometric or PIN prompt on your device. Its suggested alternative is delegation: you sign in with the passkey, then give the agent a limited, short-lived access token for specific actions. That is how many apps with proper integrations already work. Standards for agents are being drafted, but the same post says some of the more ambitious ideas are still at the research stage, so treat that as direction, not something you can use today.
The practical result is that a site with an official connection to the agent’s maker is easier to work with than a site the agent has to log into like a person. If a service offers a proper integration, use that instead of letting a browser agent sign in.
What a logged-in agent can be tricked into doing
The reason vendors pause at logins is the same reason you should care: an agent that’s signed into your accounts can be misled by what it reads.
The risk is called prompt injection. An attacker hides instructions on a web page, and an agent that reads the page may follow them. TechCrunch’s reporting in October 2025 quoted Brave’s head of privacy and security calling indirect prompt injection a “systemic challenge facing the entire category of AI-powered browsers,” and OpenAI’s security chief saying it “remains a frontier, unsolved security problem.” Early attacks hid text on a page. Newer ones hide instructions in images.
What makes this worse when you’re logged in is the reach. An agent with an open email session or a bank tab can do things a logged-out one can’t. A security researcher at Wiz told TechCrunch in a later report that limiting logged-in access “primarily reduces exposure.”
The vendors’ own numbers show the problem hasn’t gone away. In testing Anthropic published for its Chrome extension, a deliberately targeted attack succeeded 23.6 percent of the time without safeguards, across 123 test cases, and 11.2 percent with them. Those are company-reported figures from its own test set. OpenAI said in December 2025 that prompt injection, “much like scams and social engineering on the web, is unlikely to ever be fully ‘solved,'” as TechCrunch reported. Its own advice was to limit logged-in access and give agents specific instructions instead of broad ones like “take any action needed” on your inbox.
Agents also stumble on ordinary screens, apart from any attack. We covered those failures, including the pop-ups that stopped agents in Carnegie Mellon’s simulated office, in our look at what AI agents can actually do.
What the court decided about agents and login
Websites don’t always want agents inside, even when you’ve invited one in. That dispute went to court.
Amazon sued Perplexity in November 2025 over its Comet browser, which logs into accounts and buys things for users. On March 9, 2026, Judge Maxine Chesney granted a preliminary injunction, relying on an earlier Ninth Circuit case, Facebook v. Power Ventures, which held that a platform can revoke a third party’s access even when users share their credentials. Jones Day’s summary describes the effect: the platform’s say-so would outweigh the user’s.
The Ninth Circuit reversed course on August 4. In its opinion, the panel vacated the injunction and said Amazon was unlikely to win under the federal computer fraud law. The reasoning was that the statute covers someone who “intentionally accesses” a computer, and the court called the shopping assistant “a tool, not a person.” In its view, the user accessed Amazon with the assistant’s help, and Perplexity’s servers never directly contacted Amazon’s.
Three limits keep this from being a blanket win for agents. It’s a ruling on a preliminary injunction, and the case goes back to the lower court. The panel said it wasn’t setting up a legal regime for agentic AI, and it left open whether Perplexity could be liable on other theories or on different facts. And it noted Amazon can still control access through its terms of service. A site can ban agents in its terms, block them technically, or both, even if the computer fraud law doesn’t reach them. The dispute also turned partly on Perplexity’s choice not to use a user-agent string that would have let Amazon identify and block the assistant.
For you, that means an agent logging into your Amazon account isn’t a federal crime on this record, but the site may still close your account if its terms say agents aren’t allowed. Check the terms before you hand over anything you can’t afford to lose.
A safer way to give an agent access to a login
If you want to use one, these habits cover most of the risk:
- Use the takeover or handoff option rather than typing credentials into a chat.
- Keep agents away from banking, health and email accounts, which is what security researcher Rachel Tobac advised in TechCrunch’s report.
- Turn on two-factor authentication for any account an agent might touch, so a leaked session isn’t the end of it.
- Give narrow instructions: “find the invoice from March,” not “handle my inbox.”
- Sign out and clear the agent’s saved sessions after a sensitive task.
- Where an official integration exists, use it instead of a browser login. For payments, see whether an agent ever sees your real card number.
Frequently Asked Questions
Can AI agents log in to websites?
Yes, but the main products usually pause at the login page and ask you to type your password or approve a code yourself. Once you’re signed in, the agent can keep working in that session.
Do AI agents see my passwords?
It depends on the tool. OpenAI says its agent doesn’t capture what you type during takeover, and Google says it doesn’t share your passwords with Gemini in Chrome. Both are the companies’ own statements.
Can an AI agent get past two-factor authentication or a CAPTCHA?
Not on its own in the products described here. Codes sent to your phone or inbox, passkeys and CAPTCHAs are designed to prove a person is present, so agents stop and hand control back.
Is it safe to let an AI agent use my logged-in accounts?
It carries real risk. Hidden instructions on a web page can steer an agent, and OpenAI says this is unlikely to ever be fully solved. Limiting which accounts the agent can reach reduces the exposure.
Is it legal for an AI agent to log in for me?
On the Ninth Circuit’s August 2026 ruling in Amazon v. Perplexity, the federal computer fraud law likely doesn’t cover it, because the court treated the assistant as a tool used by the person. The site can still ban agents in its terms of service, and the case isn’t finished.
Can websites block AI agents from logging in?
Yes, through technical blocks, CAPTCHAs and terms of service. The Ninth Circuit noted that Amazon can still regulate access through its terms.
